Required
A current provider privacy and retention policy has been reviewed
Confirm storage, training use, deletion, and subprocessors.
Safety guide
Is ai api safe to use depends on the provider, the data you send, and the controls around each request. Use this guide to separate manageable API risk from situations that need stronger safeguards.
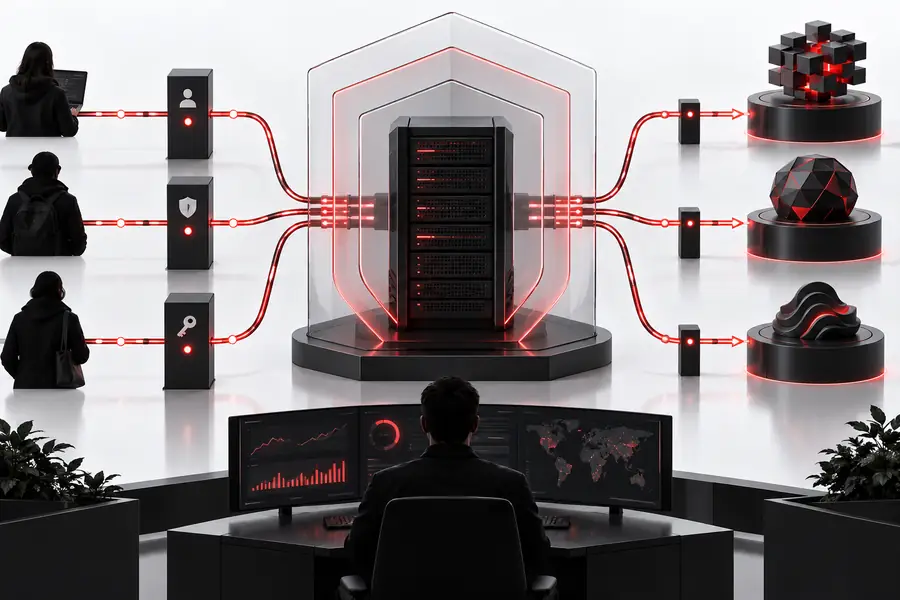
The short answer
The safest decision starts by replacing broad assumptions with specific checks about data, access, and output.
Know the limits
An AI API is a remote interface: your application sends a request to a provider, the provider processes it, and a response comes back. Safety depends on the full path, not just the model.
Your prompt may be logged, retained, reviewed, or used under terms that differ from your assumptions.
WorkaroundRead the provider's current data policy, disable retention where available, and remove unnecessary personal or proprietary details.
Models can produce confident errors, unsupported claims, or unsafe instructions even when the request succeeds technically.
WorkaroundAdd validation, citations, structured outputs, and human review for decisions with meaningful consequences.
A key embedded in browser code, a public repository, or a client app can be copied and misused.
WorkaroundKeep secrets server-side, restrict permissions, rotate them after exposure, and monitor request activity.
The API usually does not know whether a person is authorized to submit the data in a prompt.
WorkaroundApply application authentication, authorization, input filtering, and audit logging before the request is sent.
Before you connect
Treat these requirements as a minimum operating checklist rather than a guarantee. They reduce avoidable exposure while leaving room for provider-specific review.
Confirm storage, training use, deletion, and subprocessors.
Never place it in frontend or public repository code.
Redact names, identifiers, credentials, and confidential fields.
Use separate credentials for development and production.
Required for customer-facing or consequential workflows.
Strongly recommended before production traffic.
Continue carefully
Use these adjacent guides to turn a general safety review into an implementation plan.
This guide explains how to store, scope, rotate, and monitor credentials used by an AI API.
Start with the request-and-response model if you need the basic vocabulary before reviewing risk.
Compare provider capabilities and policies before selecting the service behind a sensitive workflow.
Make the call
The right level of control follows the sensitivity of the data and the cost of a wrong answer.
1
Use a server-side key, basic rate limits, redaction, and manual review.
This keeps experimentation practical while preventing the most common leaks and accidental misuse.
2
Choose a provider with suitable contractual and retention controls, then add minimization, access logging, and output checks.
Provider policy alone is not enough; your application still determines who can send data and see responses.
3
Do not make the model the final decision-maker; require qualified human judgment and domain-specific controls.
The harm from an incorrect answer can exceed the convenience of automation.
Our safety promise
A responsible AI API workflow is designed to limit exposure before a request leaves your application.
We favor the smallest useful prompt, the narrowest permission, and the shortest practical retention period. Those choices make failures easier to detect and contain.
No API can remove every risk. The goal is transparent handling, deliberate review, and a clear human owner for anything that matters.
See the difference
Safety improves when the application filters what leaves the system and checks what comes back.
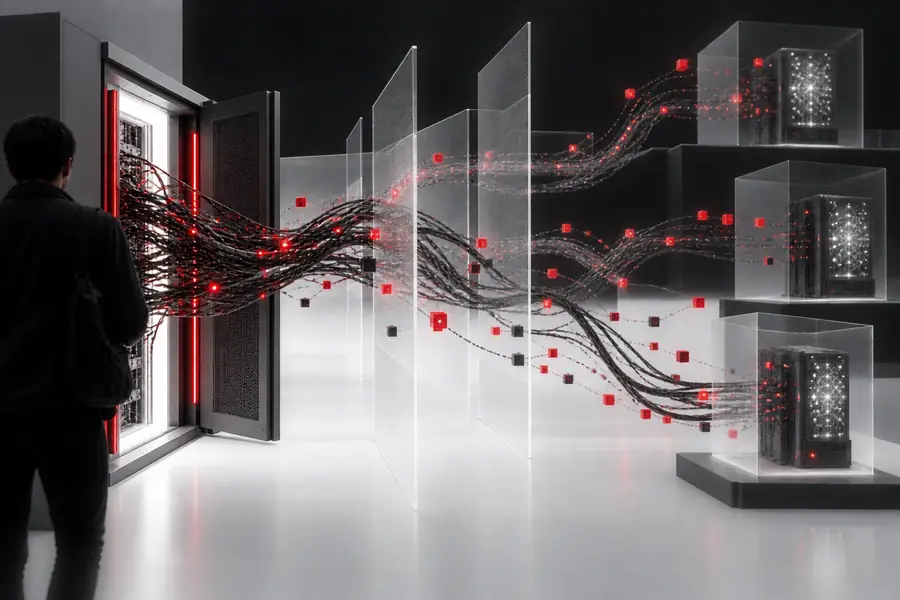
The safer pattern adds boundaries before automation.
How practice evolved
Modern API safety is the result of several familiar engineering practices being applied to model-based systems.
Teams moved credentials out of source code and into environment variables, vaults, and deployment controls.
Data minimization, retention questions, and access logging became routine parts of cloud service selection.
Applications began adding moderation, validation, fallbacks, and human review instead of treating generated text as authoritative.
Organizations formalized prompt redaction, provider evaluations, model monitoring, and policies for sensitive use cases.
A provider is one part of the control surface; secure architecture, clear ownership, and ongoing testing complete the workflow.
Take the next step
Start with a low-risk request, confirm how the provider handles data, and keep credentials and sensitive inputs behind your own application controls. When the consequences are serious, add qualified human review before launch.
Your questions
These answers give a practical starting point for deciding whether a particular integration is appropriate.
It can be, but only when the provider's privacy, retention, and contractual terms fit the information involved. Minimize or de-identify personal data, restrict access, and avoid sending details that the workflow does not need.
Possibly. Providers may process, log, retain, or review prompts according to their service terms and configuration. Check the current data-use policy rather than assuming that an API request is private by default.
No, not as a general practice. Client-side keys can be extracted and reused by others, so requests should normally pass through a protected server that applies authentication, limits, and monitoring.
An AI API can assist with analysis or drafting, but its output may be inaccurate, biased, or incomplete. For decisions involving safety, rights, health, money, or legal consequences, keep a qualified person responsible for the final judgment.